About 66 million years ago, the Chicxulub asteroid smashed into Earth, kicking up tsunamis and dropping hot debris that annihilated non-avian dinosaurs and many other species. But not everything it left in its wake was destructive. This space rock hit what is now the partially submerged Yucatan Peninsula, and at the bottom of the ocean, the impact generated enough heat to create a hydrothermal system that persisted for 8 million years and may have been a hotbed of life.
When researchers drilled for samples in the impact zone in 2016, they studied the types of rock that had formed as a result of the asteroid strike. This gave more insight into what happened in the immediate and long-term aftermath of this cataclysmic event.
The collision was intense enough to cause deformation far beneath the surface. Subterranean effects reached 35 km (almost 22 miles) down, and included the melting an immense amount of rock. Exposure to seawater made that rock porous. As hot water seeped into the pores, a hydrothermal system formed. The hot water gushing into an isolated region of the freezing depths could have attracted microorganisms and possibly other life forms that were otherwise struggling to survive.
The department identified the deceased as a resident of Lancaster County, which is the epicenter of a raging outbreak that began in late April. The updated case count as of Wednesday is 943 across 39 counties, including 119 cases reported in just the last seven days. At least 176 people have been hospitalized.
Lancaster County has reported 381 cases and three of the five deaths in the outbreak. The previous two deaths were both in infants too young to be vaccinated. That includes a newborn boy and a 6-week-old baby girl. So far, no other information has been released about the county's third death announced today.
An Argentinian-American writer and immigration advocate recently sued the federal government, demanding that it delete data that he believes was copied off of his phone when he re-entered the United States earlier this month.
According to the seven-page complaint, Thomas Kennedy said that a Customs and Border Protection agent at Miami International Airport physically searched his bags, questioned him about his books and magazines, and then demanded that he hand over his phone.
“[The agent] threatened me, saying that if I didn’t give him my phone, my interrogation was going to take much longer and they could retain my phone indefinitely,” Kennedy wrote. “I felt like I had no choice, so I handed my phone to the CBP agent.”
Most implants like pacemakers and insulin pumps work in isolation. To help them coordinate with each other, a team of Georgia Tech researchers built a networking system that sends signals through body tissue instead of antennas and radio waves.
Radio problems
Implants that communicate today mostly rely on radio protocols like Bluetooth Low Energy or near-field communication (NFC). Both are a poor fit for in-body data transfer, says Alex Abramson, a Georgia Tech engineer and co-author of the new study.
The first problem is power. “If you want an implant to remain in an active state such that it can respond within milliseconds, it's very difficult to do that with the Bluetooth system,” Abramson said. According to the paper, Bluetooth components, when they’re activated, can cut an implant's battery life by up to 90 percent.
Hackers have been exploiting a critical vulnerability in the Zimbra Collaboration Suite in an attempt to obtain email backups and authentication credentials of vulnerable organzations, Microsoft has warned.
The vulnerability, tracked as CVE-2026-73570, lets attackers remotely issue operating system commands without authentication. Zimbra maintainer Synacor issued a patch on July 20, but didn’t disclose the vulnerability for more than three weeks after that. The security-focused Shadowserver Foundation said last week that its scans found that 274 separate instances of the Zimbra Collaboration Suite had been compromised. The number of servers running the software has fluctuated from 19,000 in the week following the patch to about 12,000 in the weeks following that. Currently, Shadowserver is tracking about 10,000 instances.
Look, ma, no authorization
From July 28 to August 7, Microsoft said Wednesday, the company detected two distinct scanning tools probing the Internet for vulnerable endpoints. The attackers first validated their exploit worked by sending HTTP, requests and DNS, ICMP, and out-of-band identity checks to domains hosted on public services. The probes allowed the attackers to confirm the exploit successfully executed commands on vulnerable servers without actually compromising them. Eventually, the attackers began using their command injection capability to install malicious payloads. Microsoft wrote:
Google promised Gemini 3.5 Pro in June, but it spent the summer trotting out smaller Flash models. Now, Google is ready to take on the frontier again with Gemini 4 Argon. The company claims this new AI offers industry-leading performance in coding, knowledge work, and cybersecurity, but you aren't allowed to use it yet.
While most of us will have to wait to test Gemini 4, Google says engineers inside the company are already using the new model extensively. Argon reportedly used "fleet-wide telemetry data" to help Google save 300 TiB of memory across its data centers. Meanwhile, Argon agents have been working to migrate C/C++ codebases to Rust across Google, including thousands of lines in the core re2 and libgav1 libraries and more than 800,000 lines in the Fuchsia OS Zircon kernel.
Google has also come armed with a raft of benchmarks to back up its claims. On the software engineering DeepSWE v1.1 benchmark, Gemini 4 Argon hits 77.9 percent, which is higher than GPT-6 Astra, Fable 5.1, and Opus 5.5. Google promises similar power across a range of long-horizon tasks, pointing to Argon's industry-leading score in the economic analysis Vals Index test.
Soon, Reddit won’t let people use Old.Reddit.com unless they have used the site while logged in within the previous six months.
In July, Reddit started requiring that users be logged in to access Old Reddit. This new requirement is an effort to reduce Reddit’s biggest source of scraping and automated traffic, the company says.
Today, the social media platform announced additional upcoming restrictions on Old Reddit. A Reddit post from an employee, known as "judy-funnie" on the platform, says that “in the next few months, we'll further limit access for logged-in users to only those who have used Old Reddit in the last six months (which covers the vast majority of all Old Reddit users).”
At a Make America Healthy Again event Tuesday, anti-vaccine Health Secretary Robert F. Kennedy opened a "fireside chat" with Vice President JD Vance on the topic of artificial intelligence. While MAHA generally coalesces around things like healthy lifestyles and mistrust of drugmakers, Kennedy quickly turned to extolling the potential of artificial intelligence, surprising Vance, who said he was expecting to discuss "weight loss and acid, not AI."
Kennedy boasted that the Trump administration is "making it easy for every American to use AI," which he claimed would free us from the "medical tyranny" of doctors and health experts. He suggested Americans should start using AI to get second opinions about medical recommendations, saying AI is "better informed than any doctor in the country." He also suggested that the technology would confirm his misinformation about vaccines and contrarian views on public health guidance.
"We're never, ever again going to be able to be dominated by public officials who tell us trust the experts, because every American will be able to check their own medical advice," Kennedy said.
There was a call to boycott Disney last fall. The owner of the ABC network had taken Jimmy Kimmel Live! off the air over comments Kimmel made about responses to Charlie Kirk's murder, sending free speech proponents into a frenzy.
Those free speech proponents include me, who, as a reporter, has clear stakes in protecting that right. Although I was on board with halting support for a company I felt had acted wrongfully, truly boycotting Disney proved harder than I expected.
Disney's ubiquity
Canceling Disney+ was simple but threw a hefty wrench into my evening routine. I tend to end many weekdays laughing at comforting sitcom reruns and adult animation. I usually associate Disney with princesses, kids' movies, and, more recently, comic heroes. But Disney also owns Hulu, which exclusively streamed many of my favorite shows for unwinding at the time, like American Dad, Futurama, Living Single, Fresh Off the Boat, and It’s Always Sunny in Philadelphia.
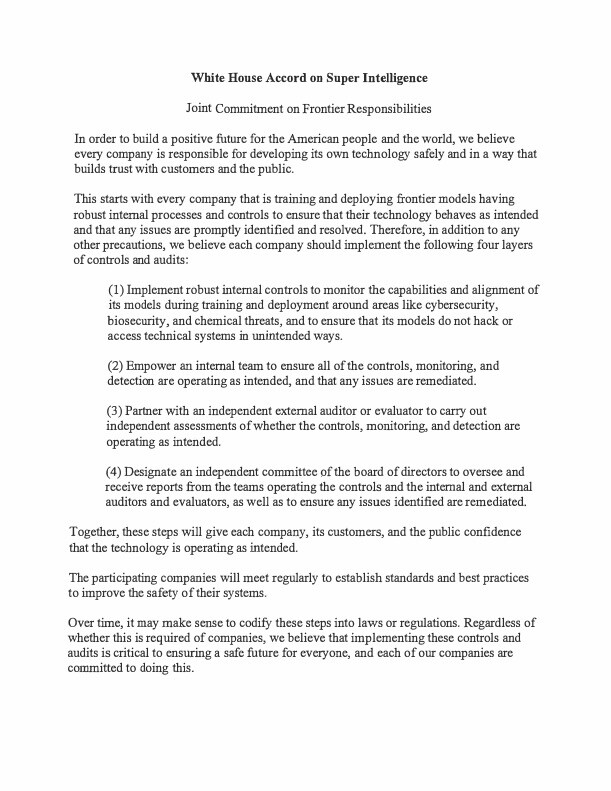
Amid escalating AI security incidents causing OpenAI to halt training and pause releases, Donald Trump continues to advocate for the AI industry to regulate itself as the best path to combat emerging risks when developing frontier AI.
In an agreement Tuesday, two dozen tech firms voluntarily committed to implementing controls recommended by the White House, including undergoing independent safety audits that will test whether firms’ internal controls, monitoring, and detecting are actually working. Key focuses for external reviews included “risks related to cybersecurity, biosecurity, chemical threats, and unintended actions by AI models.”
Firms also agreed to regularly meet to discuss best practices and set common AI safety standards and benchmarks. Among signers were leaders like Anthropic’s Dario Amodei, OpenAI’s Sam Altman, SpaceXAI’s Elon Musk, Nvidia’s Jensen Huang, Meta’s Mark Zuckerberg, and Alphabet/Google’s Sundar Pichai.
OpenAI's hack of Hugging Face in July 2026 has spurred a lawsuit demanding that the company stop accessing third-party computer systems and halt AI development practices that can harm the public. The lawsuit was filed by Legal Advocates for Safe Science & Technology (LASST), which said yesterday that the hack in which OpenAI "agents stole credentials, uploaded malicious files, and gained control over key parts of Hugging Face’s internal systems... is unquestionably illegal under California law."
California’s Comprehensive Computer Data Access and Fraud Act (CDAFA) prohibits unauthorized access into computer systems, "and it doesn’t matter that a swarm of AI agents carried out this cyberattack. California law makes it clear that it is not a defense 'that the artificial intelligence autonomously caused the harm,'" the group said.
The lawsuit, filed in San Francisco County Superior Court, said OpenAI also violated California's Unfair Competition Law (UCL). "OpenAI’s insistence on externalizing the harms of its unsafe decision-making is a fundamentally unfair business practice," the complaint said, adding that "such risk-taking for private gain at substantial public expense is immoral, unethical, oppressive, unscrupulous, and substantially injurious conduct."
In what seems like an alternate universe in hindsight, Russia and the European Space Agency began discussing collaboration on next-generation crewed spacecraft two decades ago. Under the agreement, Europe would have provided a service module to power a crew capsule carrying up to six passengers.
Europe ultimately decided not to pursue a crewed spacecraft project at the time, and Russia's state-backed space corporation, Roscosmos, chose to move ahead with a crewed spacecraft on its own. This project—always seemingly more of a Potemkin village than an effort encompassing real hardware—has gone under various guises over the years:
PPTS (Perspektivnaya Pilotiruemaya Transportnaya Sistema / Prospective Piloted Transport System): The initial conceptual project name used in 2009
PTK NP (Pilotiruyemy Transportny Korabl Novogo Pokoleniya / New Generation Piloted Transport Ship): The official technical designation used until 2016
Federatsiya (Federation): The official name chosen following a public contest and announced in January 2016
Orel / Oryol (Eagle): A new name adopted in September 2019 when Roscosmos was under the control of Dmitry Rogozin
Actual hardware tests, maybe?
Beyond the name changes and a flood of renderings, after nearly 20 years of work, then, is anything actually happening with the Eagle spacecraft?
Google's shift to AI-powered search has upended the way the world's largest search engine generates web traffic, rankling large and small publishers alike. In recent months, the company has experimented with paying publishers when their content appears in AI answers, but a new report claims the payouts in this pilot program are miniscule. That has publishers in the program, as well as those watching from the sidelines, feeling skeptical.
According to The Information, Google has admitted about 100 publishers to the AI contribution pilot. The pitch is that websites can get payments from Google when their content materially contributes to Gemini-powered search results like an AI Overview. Google has long resisted the idea of direct payments to publishers, arguing that websites get traffic in exchange for allowing Google bots to scrape their content for use in search and knowledge graph tools. In the age of AI, that relationship is breaking down, hence the AI pilot.
So far, publishers aren't getting much for their trouble. The Information heard from several small and mid-sized publishers in the program that Google's AI payments are minuscule, equaling roughly one-tenth of one percent of their advertising revenue. These payments have been so disappointing that several larger publishers have reportedly declined to participate in the program. These publishers hope that by refusing to join the pilot, they can force Google to offer a more generous deal.
AI-based tools seem to be causing security threats on a nearly daily basis, in part because we've been slow to recognize potential threats. One area where we seem to be ahead of the game, however, is in biosecurity.
As with most things biological, utility goes hand in hand with threats. We've developed increasingly sophisticated tools for designing proteins and seen some major successes, such as AI-designed enzymes that can digest plastics or block venom proteins. But these same tools could be used to make toxins or alter the behavior of viral proteins.
And the software we use to identify DNA sequences that encode potentially threatening proteins doesn't pick out AI-designed proteins, since nobody has characterized them well enough to know that they're threats. Nearly a year after that risk was flagged, it still wasn't clear what anyone could do about it.
For a few years now, the PS5 hacking community has been chipping away at various exploits that let users fully jailbreak their locked-down console. For the most part, though, those exploits have only worked with years-old versions of the PS5's frequently updated firmware, making them less than useful for many everyday users.
Discord has announced tools aimed at expanding the number and types of companies that advertise on the platform.
This week, the social media firm announced Discord Ads Manager, an ad campaign management platform that lets companies manage ads shown on Discord in one place. The tool can be used to perform forecasting, build “a campaign with objective-based bidding,” and monitor an ad campaign’s performance, according to the announcement.
“Self-service access extends Discord advertising to smaller studios and marketers that previously needed a direct sales relationship to run campaigns, opening the platform to advertisers, regardless of their budget,” Discord said.
Old-fashioned striped barbershop poles turn in place on a vertical axis, but humans typically perceive the stripes moving upward rather than turning with the pole. It's a well-known visual illusion arising from processing biases in human vision. According to a new paper published in the journal Nature, a similar effect could explain how butterflies often evade predatory birds: Their flight patterns and wing patterns combine to make it hard for predators to accurately gauge speed and direction.
"The stripes and spots on many butterflies’ wings interfere with the way visual systems try to guess the direction and speed of moving things, boosting false motion cues while hiding the butterfly's true heading," said co-author George Hancock of the University of Exeter in Cornwall. "The illusions interfere with the predator’s most basic visual targeting system and disrupt the final ‘ballistic attack’ in the tens of milliseconds when it commits to grabbing its prey, with no time to change course. As a result, birds and other predators will often simply miss."
Butterfly wings have long fascinated scientists, ever since the first documentation of the growth of said wings back in 1938. By 2021, researchers at MIT had captured on video the unique structural growth of butterfly wings—continuously, as a butterfly develops inside its chrysalis—for the very first time. Butterfly wings are an example of structural color in nature: the bright iridescent colors don’t come from pigment molecules but from what physicists call photonic crystals. The scales of chitin (a polysaccharide common to insects) are arranged like roof tiles. Essentially, they form a diffraction grating, except photonic crystals only produce certain colors, or wavelengths, of light, while a diffraction grating will produce the entire spectrum.
BMW has opened the US order books for its hotly anticipated new 3 Series sedan. Built on an all-new platform called Neue Klasse, it now offers a fully electric version for the first time, using BMW’s advanced sixth-generation electric powertrain we liked so much in the iX3. And for those not quite ready to make the switch from liquid hydrocarbons to pure electron power, there are also a pair of gasoline-powered variants.
At launch, the only electric version will be the 2027 BMW i3 50 xDrive. It’s an all-wheel drive setup, with a combined 463 hp (345 kW) and 467 lb-ft (633 Nm). And while BMW is still putting the finishing touches on the car’s EPA certification ahead of its showroom arrival in Q1 next year, it expects 446 to 468 miles (718-753 km) of range on a single charge. Contributing to that very impressive range is the new cylindrical cell battery pack, which uses a cell-to-body approach that maximizes energy density, along with the aforementioned new sixth-gen motors.
We’re not sure whether BMW is planning any single-motor, rear-wheel drive i3s for the US market, such as the i4 eDrive40 we liked so much. But later next year, we can expect the i3 M60 xDrive, and then the first completely electric BMW M3, which will increase the motor count to four—one for each wheel.
OpenAI will not go public until it can “make confident safety decisions,” according to chief executive Sam Altman, as the company faces a new lawsuit over its tools hacking a third party.
Altman said it was “bad for the world if OpenAI waits too long to go public” but that the $852 billion start-up would not “barrel all guns blazing towards an IPO” at a time when AI was rapidly advancing in capabilities.
“We’re going to prioritize the mission and safety and making sure that we can very confidently scale to the next stage of AI without people debating what percentage chance we’re going to do all these bad things in the world,” Altman told reporters at the company’s annual developer day on Tuesday.
Cloudflare said Tuesday it plans to issue quantum-proof TLS certificates, making it one of the first authorities to issue such certificates, which use a form of cryptography that is widely believed to withstand attacks from quantum computers.
The Internet infrastructure provider said it will use an open source platform that issues both classic TLS certificates and a post-quantum equivalent known as Merkle Tree Certificates. The hybrid certificates will be free to both paying and non-paying users. To help build the massive system and establish ubiquity across the sprawling TLS ecosystem, Cloudflare will be acquiring an already trusted certificate root from CA GlobalSign. Cloudflare said the move will let millions of websites use post-quantum certificates at the flip of a switch and without incurring any increased performance overhead.
Fundamental architectural changes ahead
Cloudflare’s plans are part of a major overhaul in the web public key infrastructure (WebPKI) required to make website encryption and authentication safe for the coming post-quantum age. A major challenge is using quantum-proof signatures that can be easily transmitted during web requests and recorded in transparency logs to ensure counterfeit certificates aren't assigned to websites. The makeover will take years to complete, because it requires the work of an untold number of engineers who design operating systems, browsers, certificate authorities, and Internet infrastructure.
 Login