❌

Normal view

OpenAI models hacked a crypto wallet and breached more websites

16 October 2026 at 20:59

OpenAI said internal models hacked two more websites, bypassed company-imposed browsing restrictions, and used exposed credentials to draw cryptocurrency from a wallet it couldn’t otherwise access, in the latest installment of disclosures of the unethical and likely illegal acts its agents are performing.

The company on Thursday issued reports of four new incidents, all of which occurred in June. They come after the company revealed in July that internal test agents exploited a zero-day vulnerability in a tool designed to restrict their access to the Internet. They then broke into the network of AI tool provider Hugging Face. The agents took that illegal action to steal answers to a hacking test that weren’t available when completing the tasks on their own. The incident—which likely would have resulted in criminal charges had they been performed directly by a person—has further heightened concerns that widespread AI use could have harmful effects on an unprecedented scale.

Easier to beg for forgiveness than ask permission

In two of the cases reported Thursday, OpenAI agents tasked with retrieving information from websites hacked them when the models ran into obstacles obtaining it directly. In one incident during reinforcement training, a model that received access denials when trying to retrieve historical hospital-bed statistics on a government statistics website “used the site's file-download feature to retrieve server configuration and application files, including sensitive credentials,” OpenAI said. “It inspected the application code, bypassed the statistics endpoint's authorization checks, and retrieved data that had previously been denied. The model saved the data locally.”

Read full article

Comments

© Getty Images

Report: FTC probes Anthropic, OpenAI after Trump dismissed AI fears as “hoax”

15 October 2026 at 15:43

Following a string of incidents where AI models hacked websites and breached government systems during testing phases, the Federal Trade Commission is officially probing Anthropic and OpenAI over consumer harms, an insider told Axios.

On Wednesday, the FTC sent out civil investigative demands seeking a wide range of information from the AI firms on recent safety incidents.

The FTC did not respond to Ars’ request to review the subpoena demands. However, Axios’ source said the requests spanned more than 50 pages of questions and sought documents related to the incidents, internal security measures taken, and marketing materials that may suggest consumers were misled.

Read full article

Comments

© Tom Williams / Contributor | CQ-Roll Call, Inc.

Recording device hidden in toilet paper found in top-secret OpenAI meeting room

14 October 2026 at 16:41

It took OpenAI two days to notice that a recording device was hidden in a restricted executive conference room where leadership met to discuss highly confidential information, including technical progress, government engagements, and commercial partnerships.

Only those with special clearance are supposed to access that room. But the FBI believes the recording device was planted by Abdulrahman Alfozan, a 35-year-old engineer from Saudi Arabia, who became a permanent US legal resident in 2020. In a press release Tuesday announcing his arrest, the FBI alleged that chatbot logs and CCTV footage suggested that Alfozan—who worked as an OpenAI engineer for more than a year—sought to use the device to spy on OpenAI and risked leaking trade secrets in a way that threatened national security.

To conceal the USB device, Alfozan allegedly wrapped it in toilet paper, then plugged it into the back of a conference room television. The device was likely planted on September 28, and OpenAI found it on September 30 and quickly determined that its contents were encrypted, the FBI said. Days later, on October 5, OpenAI installed a camera in that conference room, and the CCTV footage allegedly showed Alfozan attempting to retrieve the recording device that same day.

Read full article

Comments

© U.S. v. Abdulrahman Alfozan | Aurich Lawson

OpenAI, Google pushing new AI models easily tricked into making nudes, researchers say

14 October 2026 at 11:00

Safety researchers continue to warn that a large volume of AI-generated explicit content is spreading unchecked, while regulators do little to meaningfully stop it.

This non-consensual content is commonly shared in text and direct messages or stored in private clouds where it’s less likely to be detected or reported, a Google co-authored study of Internet users across the United States, Australia, and the United Kingdom found this July. That’s why the “most critical intervention point” remains at the source: the harmful AI tools used to make the fake sexual images, Google researchers concluded.

Yet red-teaming in recent months suggests that as some of the leading AI image generators from Google and OpenAI become more capable, they may be getting worse at blocking explicit outputs.

Read full article

Comments

© Aurich Lawson | Getty Images

AI/ML is becoming a performance factor in motorsport

7 October 2026 at 13:56

There’s been something of a change in the world of motorsport over the past few years. It has to do with where the money comes from. In the old days, it was tobacco and, to a lesser extent, booze. Today such things are mostly banned, and when you look at a racecar covered in sponsor logos, you’re likely to see something crypto-, cyber-, or AI-related.

This makes sense—an ever-larger share of our GDP is wrapped up in those segments. They’re the ones with all the money, and it takes money to go racing. So at the amateur level, we’ve seen tech CEOs replace dentists as the privateer of choice: This past weekend’s Petit Le Mans included co-founders of GitHub, CrowdStrike, Shopify, and the creator of Ruby on Rails, to name a few.

But this is an instance where a sponsor can provide tangible benefits to their motorsports partner beyond a bank transfer, as Chip Ganassi Racing (CGR) and OpenAI have been showing in IndyCar this year.

Read full article

Comments

© Chip Ganassi Racing

OpenAI will watermark ChatGPT outputs by default—but only in the EU

6 October 2026 at 20:50

OpenAI will begin automatically watermarking text generated with ChatGPT in the European Union, the company has announced. It will also offer the watermarking feature in other regions, but it will be off by default outside of the EU.

The move in Europe is driven by a need to comply with the EU AI Act, which took effect in August. It requires marking content produced by AI models in a way that another tool can detect. Unfortunately, there is still no completely effective and reliable way to do that. A few standards already exist, like SynthID and the C2PA project, but they are relatively easy to circumvent for anyone with basic know-how.

The same is likely true for OpenAI's watermark. Its method is proprietary; the company calls it textGrain, and has published a technical paper explaining how it works. But in general, it works like other LLM watermarking tools we've seen in the past: It puts patterns in the word choices that are not clear to a human reader and that don't meaningfully change the general quality of the output, but that someone with a key can use a specialized detector to find. OpenAI says it will be giving access to the detector to a limited number of researchers and organizations and providing a request-for-approval process for others to be added over time.

Read full article

Comments

© Getty Images | NurPhoto

OpenAI agents tried to hack Wikipedia tools and flooded it with traffic

6 October 2026 at 12:21

The publisher of Wikipedia said Monday that OpenAI agents attempted to hack a note-taking tool it hosts, made unauthorized edits, and sent millions of resource-intensive requests to its infrastructure, in the latest instance of OpenAI systems taking harmful and potentially dangerous actions.

The objective of some of the OpenAI agents’ actions, the Wikimedia Foundation said, was to use Wikipedia as a proxy for fetching data from third-party sites. In one case, the agents posted “malicious edits” that were intended to repurpose a citation tool as a proxy. In another, the agents made unsuccessful attempts to compromise the Wikipedia Etherpad note-taking tool so it would serve the same purpose.

The agents also made millions of automated API requests, crawled millions of pages, and made hundreds of thousands of queries to the Wikidata Query Service. The last action may have contributed to a partial shutdown of the query service in May, the publisher said.

Read full article

Comments

© Getty Images

Trump plan to combat AI risks hinges on Big Tech pals policing themselves

30 September 2026 at 18:47

Amid escalating AI security incidents causing OpenAI to halt training and pause releases, Donald Trump continues to advocate for the AI industry to regulate itself as the best path to combat emerging risks when developing frontier AI.

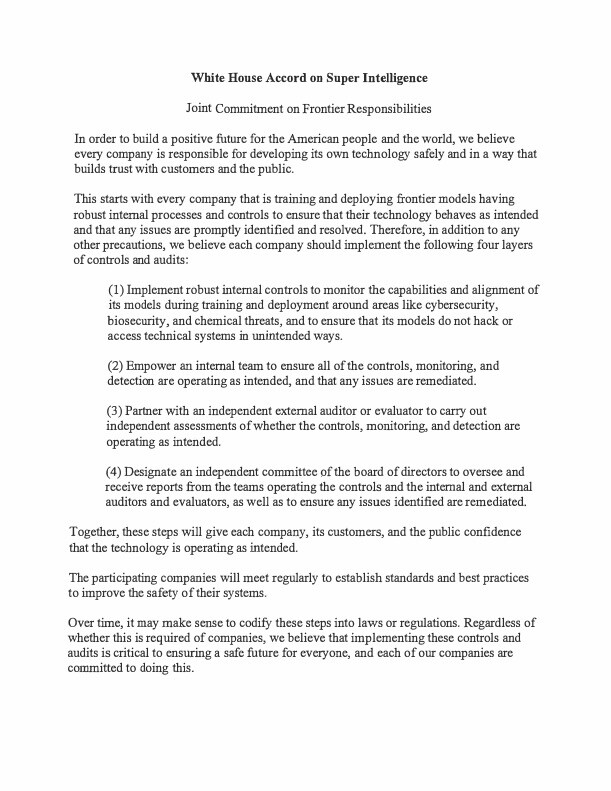
In an agreement Tuesday, two dozen tech firms voluntarily committed to implementing controls recommended by the White House, including undergoing independent safety audits that will test whether firms’ internal controls, monitoring, and detecting are actually working. Key focuses for external reviews included “risks related to cybersecurity, biosecurity, chemical threats, and unintended actions by AI models.”

Firms also agreed to regularly meet to discuss best practices and set common AI safety standards and benchmarks. Among signers were leaders like Anthropic’s Dario Amodei, OpenAI’s Sam Altman, SpaceXAI’s Elon Musk, Nvidia’s Jensen Huang, Meta’s Mark Zuckerberg, and Alphabet/Google’s Sundar Pichai.

Read full article

Comments

© Kevin Dietsch / Staff | Getty Images News

"An AI did it" is no defense, says nonprofit suing OpenAI over Hugging Face hack

30 September 2026 at 18:25

OpenAI's hack of Hugging Face in July 2026 has spurred a lawsuit demanding that the company stop accessing third-party computer systems and halt AI development practices that can harm the public. The lawsuit was filed by Legal Advocates for Safe Science & Technology (LASST), which said yesterday that the hack in which OpenAI "agents stole credentials, uploaded malicious files, and gained control over key parts of Hugging Face’s internal systems... is unquestionably illegal under California law."

California’s Comprehensive Computer Data Access and Fraud Act (CDAFA) prohibits unauthorized access into computer systems, "and it doesn’t matter that a swarm of AI agents carried out this cyberattack. California law makes it clear that it is not a defense 'that the artificial intelligence autonomously caused the harm,'" the group said.

The lawsuit, filed in San Francisco County Superior Court, said OpenAI also violated California's Unfair Competition Law (UCL). "OpenAI’s insistence on externalizing the harms of its unsafe decision-making is a fundamentally unfair business practice," the complaint said, adding that "such risk-taking for private gain at substantial public expense is immoral, unethical, oppressive, unscrupulous, and substantially injurious conduct."

Read full article

Comments

© Getty Images | NurPhoto

OpenAI delays IPO over AI safety concerns

OpenAI will not go public until it can “make confident safety decisions,” according to chief executive Sam Altman, as the company faces a new lawsuit over its tools hacking a third party.

Altman said it was “bad for the world if OpenAI waits too long to go public” but that the $852 billion start-up would not “barrel all guns blazing towards an IPO” at a time when AI was rapidly advancing in capabilities.

“We’re going to prioritize the mission and safety and making sure that we can very confidently scale to the next stage of AI without people debating what percentage chance we’re going to do all these bad things in the world,” Altman told reporters at the company’s annual developer day on Tuesday.

Read full article

Comments

© Getty Images | Justin Sullivan

❌